PhishEye Blog · Page 2 of 3

Threat research, takedown playbooks, and the operator’s view, page 2

Field notes on phishing detection, typosquat enforcement, search-threat strategy, and the takedown metrics that actually reduce customer harm — not vanity dashboards.

Latest postsPage 2 of 3

We Got Phished With Our Own Brand — PhishEye blog cover illustration

Research · · 8 min read

We Got Phished With Our Own Brand

Over 21 hours a phishing operator hit three of our own mailboxes with spoofed [email protected] emails, rotating lures and cloned login pages across IPFS and Google Cloud Storage. We tear down all three waves, the Formspark exfil, and why DMARC quarantined every one.

Read more
Chrome Extensions as Covert Web Proxies — PhishEye blog cover illustration

Research · · 8 min read

Chrome Extensions as Covert Web Proxies

15+ Chrome utility extensions (emulators, password managers, converters) embed a bandwidth-sharing SDK that quietly turns the browser into a covert web-scraping proxy via hidden iframes and five Lambda backends. Unit 42's findings, analyzed for defenders.

Read more
Device-Code Phishing Evasion Techniques — PhishEye blog cover illustration

Research · · 8 min read

Device-Code Phishing Evasion Techniques

CAPTCHA gates, multi-step SaaS chains, blob-URL delivery, and Cyrillic look-alike source obfuscation: Unit 42 documented four ways device-code phishing pages dodge automated scanners. What each one defeats, and how defenders keep up.

Read more
Rhadamanthys Stealer Returns After Takedown — PhishEye blog cover illustration

Research · · 8 min read

Rhadamanthys Stealer Returns After Takedown

A new Rhadamanthys infostealer campaign resurfaced days after a law-enforcement takedown, delivered via a cloned RingCentral download, a 385MB anti-sandbox dropper, layered DLL side-loading, and Azure Front Door C2. Unit 42's full chain, analyzed for defenders.

Read more
Grand Egyptian Museum Ticket Scam Network — PhishEye blog cover illustration

Research · · 12 min read

Grand Egyptian Museum Ticket Scam Network

Starting from a handful of fake Grand Egyptian Museum ticket sites, we mapped an industrial fake-ticket network: 188 domains impersonating ~40 real attractions across 10+ countries, on a handful of shared origin servers.

Read more
Hotel Booking Phishing: Reservation Hijack — PhishEye blog cover illustration

Research · · 12 min read

Hotel Booking Phishing: Reservation Hijack

Hackers take over real hotel accounts on Booking.com, watch the incoming reservation queue, and message each guest a fake 'complete your booking' payment link. A full breakdown of the reservation-hijack scam, with a live example we traced and reported.

Read more
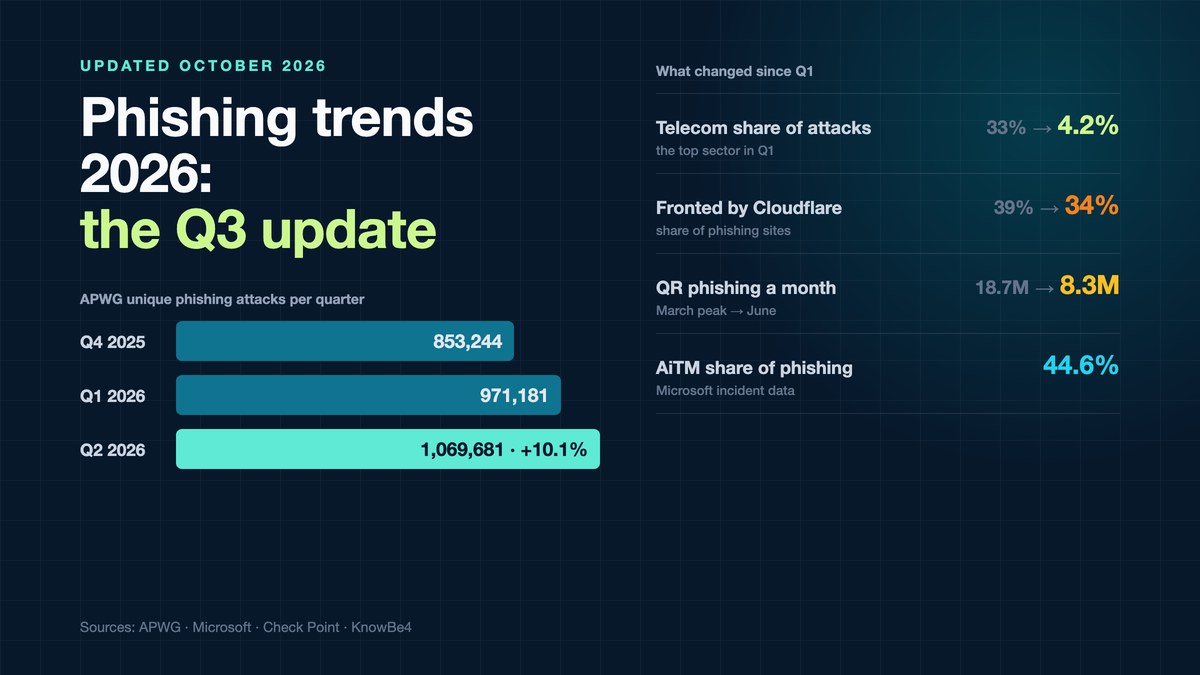
Phishing Trends 2026 Q3 update cover: APWG phishing attacks rising from 853,244 in Q4 2025 to 971,181 in Q1 and 1,069,681 in Q2 2026, beside what changed since Q1: Telecom's share of attacks 33 to 4.2 percent, Cloudflare-fronted phishing sites 39 to 34 percent, monthly QR phishing 18.7 million to 8.3 million, and AiTM at 44.6 percent of phishing techniques.

Research · · 36 min read

Phishing Trends and Statistics: 2026 Report

Microsoft, APWG, KnowBe4 and Check Point 2026 data in one picture, updated with Q2 and Q3 figures: attacks up 10.1% to 1,069,681, credential theft at 94–96%, AiTM 44.6% of phishing techniques, SaaS/webmail the top target, and Cloudflare fronting 34% of phishing sites.

Read more
SharePoint Phishing on Cloudflare Workers — PhishEye blog cover illustration

Research · · 12 min read

SharePoint Phishing on Cloudflare Workers

A live SharePoint credential-phishing chain on free Cloudflare infrastructure: a fronted lure and fake-CAPTCHA redirect into a cloaked workers.dev loader, tracked across 5+ auto-provisioned Workers accounts.

Read more
Cloudflare Drop: Instant Hosting, Phishing Risk — PhishEye blog cover illustration

Research · · 13 min read

Cloudflare Drop: Instant Hosting, Phishing Risk

Cloudflare Drop deploys a static site to a workers.dev URL in seconds with no account. We weigh the phishing-abuse risk, compare it with other free static hosts, and show why Cloudflare's own abuse-report API blocks the takedown teams fighting back.

Read more
IronToll: Global Government-Impersonation PhaaS — PhishEye blog cover illustration

Research · · 16 min read

IronToll: Global Government-Impersonation PhaaS

One live phishing URL unrolled IronToll: a 73-domain, multi-country phishing-as-a-service campaign built on the Chinese Iron Man kit, stealing credentials and live SMS OTPs. Full IOCs, C2 IPs, and the hunting method.

Read more
Social Media & Fake App Brand Protection — PhishEye blog cover illustration

Cybersecurity · · 8 min read

Social Media & Fake App Brand Protection

Defend the two channels most brand-protection programs under-serve: social media impersonation and fake mobile apps — detection, per-platform takedowns, and how to choose a platform.

Read more
PCI DSS Phishing Requirements (2026 Checklist) — PhishEye blog cover illustration

Cybersecurity · · 11 min read

PCI DSS Phishing Requirements (2026 Checklist)

PCI DSS v4.0 turned anti-phishing into a technical control. A pre-audit checklist mapping Requirements 5.4.1, 8.4.2 and 12.6 to DMARC, MFA, simulations and audit evidence.

Read more
ClickFix 2026: Fake CAPTCHA Hides C2 On-Chain — PhishEye blog cover illustration

Research · · 15 min read

ClickFix 2026: Fake CAPTCHA Hides C2 On-Chain

A live ClickFix campaign poisons your clipboard via a fake CAPTCHA and hides its C2 on the Polygon blockchain (EtherHiding) to defeat takedowns. Full chain, 97-domain IOC feed, defenses.

Read more

Stay close to the research

Subscribe to the RSS feed for new posts, or get in touch about the investigations.