GiftWatch: The Fake Smartwatch Giveaway Kit
Published 31 min read
Contents
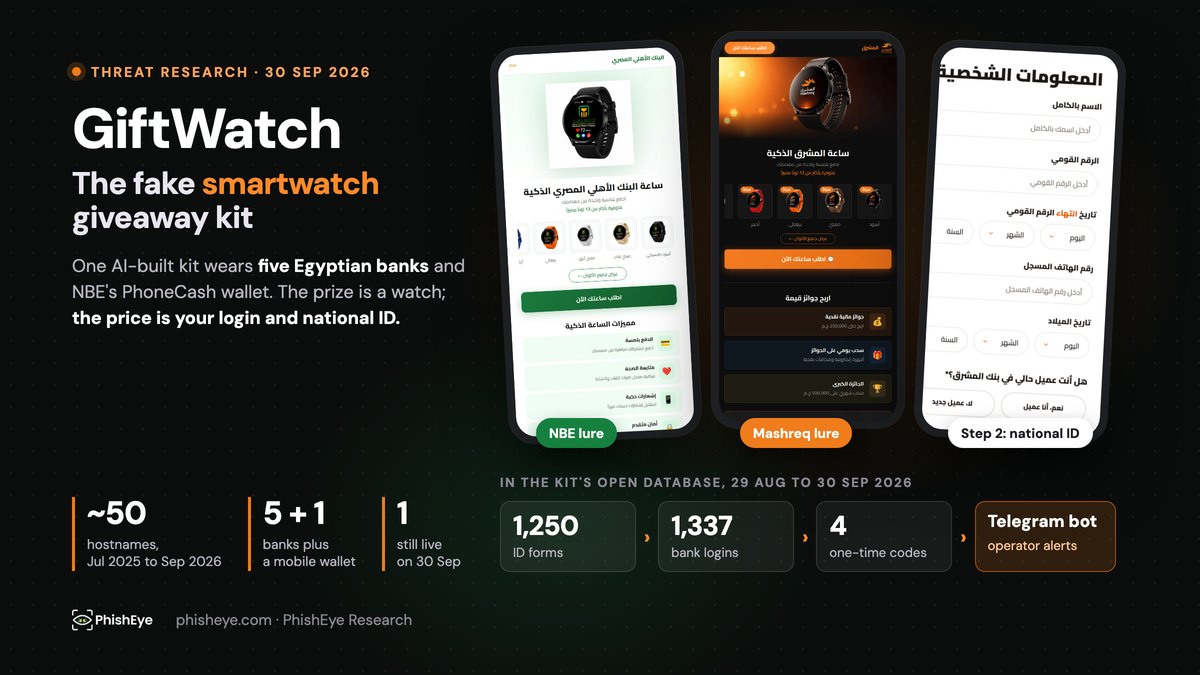
A Facebook post says your bank is giving away free smartwatches: answer a few questions and pick your colour. The page looks right, with the bank's logo, the right Arabic typography, a watch picker and a short order form. It asks for your name and national ID number, then your online-banking login, then a one-time code. The current version never asks for a payment, which removes the usual warning sign.
We spent 30 September 2026 tracking this operation, which we call GiftWatch, end to end, starting from a link reported to PhishEye. It impersonates five Egyptian banks (National Bank of Egypt, Bank Mashreq Egypt, FAB Egypt, AAIB and Housing & Development Bank) plus NBE's PhoneCash wallet, and runs a United Arab Emirates variant aimed at Mashreq's home market. We mapped about 50 hostnames used from July 2025 (a Wix pilot) to September 2026, including that pilot, an adjacent Barclays clone and one kit backend. We also reconstructed the kit's anatomy: it is built and rotated with AI site builders (Manus and Lovable), configured through a Firebase database readable without authentication, and it sends victims' credentials, personal data and one-time codes to Telegram bots. That same database held something we were not looking for: a second operation, fake Doha event-ticket shops whose "checkout" harvests payment cards, run by the same operator on the same Firebase project and Telegram infrastructure. On 30 September 2026, the bank kit and the ticket shops were both still live.
Safety notice. Every indicator in this article is defanged (
example[.]com). The Firebase project ID and the Telegram bot and chat IDs are withheld; they are being reported to Google and Telegram. Do not visit the live domains; archived scans are linked instead. See Evidence and methodology for what we did and did not do.
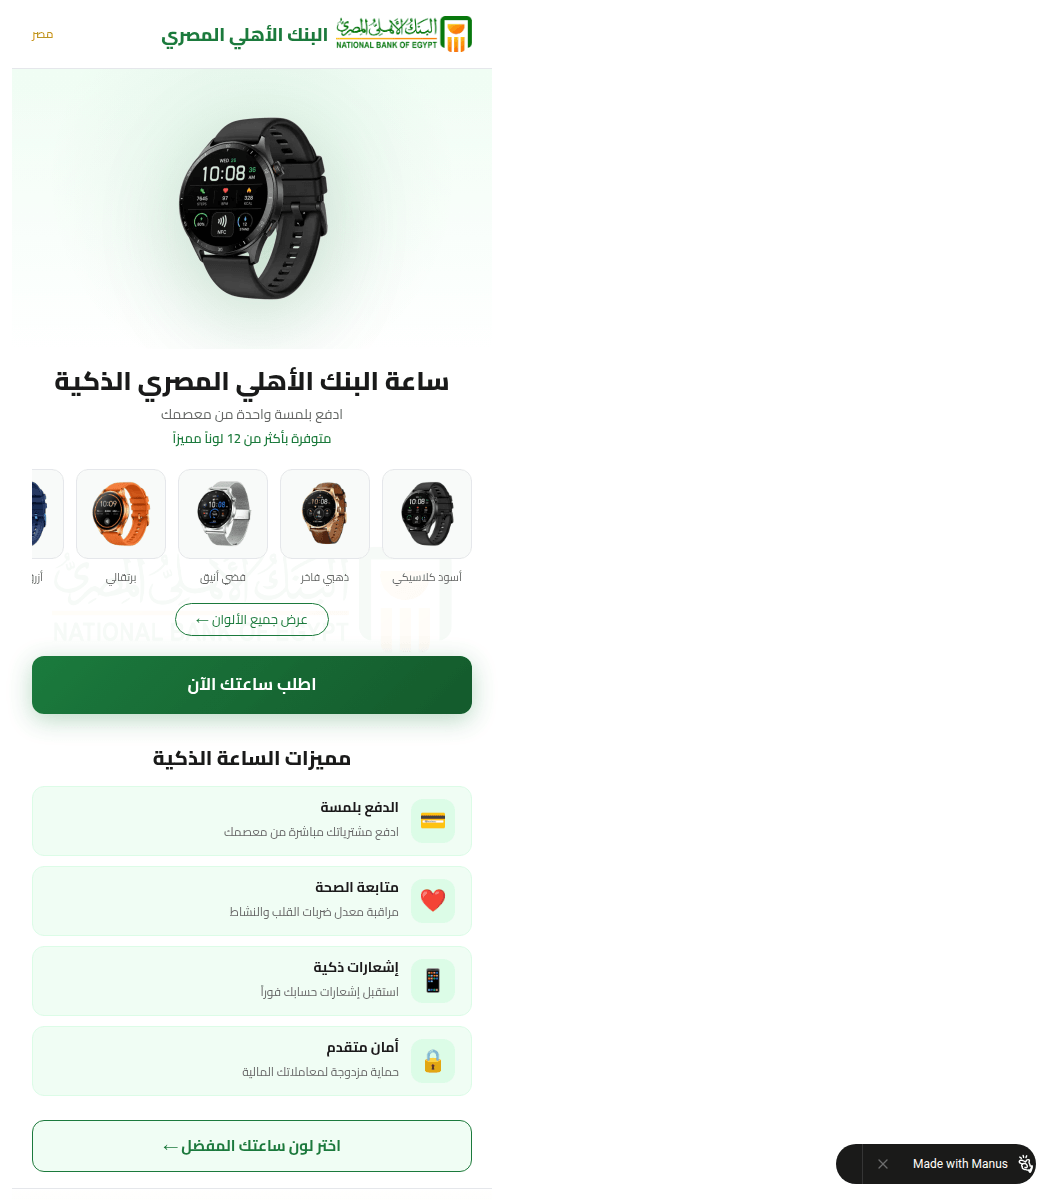
mashreqwatch-m9cuhnwa[.]manus[.]space (archived 3 August 2026, urlscan[.]io). Despite the Mashreq-style slug, this host served an NBE page; its page title reads "احصل على ساعتك الذكية" ("get your smartwatch"). The Manus builder badge is still on the page.At a glance
| Name | GiftWatch (our tracking name, after the "free gift from your bank" label the kit puts on every watch, whatever the brand) |
| Lure | Free smartwatch or cash draw from "your bank" |
| Brands | NBE, Bank Mashreq (Egypt and UAE), FAB Egypt, AAIB, HDB and NBE's PhoneCash wallet; one adjacent Barclays clone |
| Scale | About 50 bank-kit hostnames, July 2025 to September 2026, plus a five-domain fake-ticketing family active since January 2026; a new wave roughly every month |
| Kit | Config-driven React single-page app; a brand swap is a config edit |
| Built with | Manus (manus[.]space hosting and billing pages) and Lovable (__l5e assets, lovable[.]cloud nameservers) |
| Config and data | Firebase Realtime Database, readable without authentication |
| Exfiltration | Telegram bot API (three bots, two chats): credentials, personal data, one-time codes, payment-card attempts |
| Delivery | Facebook (captured URLs carry fbclid click identifiers) |
| Second vertical | Fake Doha event-ticket shops on the same Firebase project: card data and one-time codes harvested at the "checkout" (see the ticketing vertical) |
| Status on 30 Sep 2026 | 49 of 50 bank-kit hostnames not serving the kit (blocked, suspended, dropped, dead or dormant); 1 live: giftmashraq[.]com; in the ticketing vertical, ticketsdoha[.]com was also serving, and four of its five hostnames were still serving on 2 October |
The lure
Every wave uses the same pitch with a different bank stamped on top. The earliest instance we found (July 2025, on Wix) runs a draw variant: "ادخل السحب الآن" ("enter the draw now"). From June 2026 the dominant variant is the smartwatch giveaway: pick your watch colour from a grid of eight, "free gift from your bank," and complete a short order form.
The pitch is tuned for Egyptian banking customers. The banks named are among the country's best-known retail brands; the prize is small enough to seem plausible; and the ask escalates gently: personal details first, "verify your account" second, the one-time code last. The final screens mimic the bank's own online-banking login, down to Face ID copy ("تمكين معرّف الوجه") and call-centre numbers taken from the real banks' footers.
Egyptian authorities have already warned about this lure. On 23 June 2026 the Central Bank of Egypt and the Cabinet's Media Centre said that social-media posts offering free smartwatches and cash rewards "have nothing to do with banks operating in Egypt" and are built to collect card numbers, account details, passwords, phone numbers and OTP codes (Al Khaleej). Losses have followed: on 18 September 2026 Cairo 24 reported that EGP 900,000 was stolen from a merchant's bank account after a smartwatch advert on Facebook (via Nabd), and Al Arabiya reported on 1 July 2026 that an Egyptian lost money to a "gift" smartwatch offer (Al Arabiya). These reports describe the same lure but do not identify the kit or its operator, so we cannot tie any of those losses to the instances in this article.
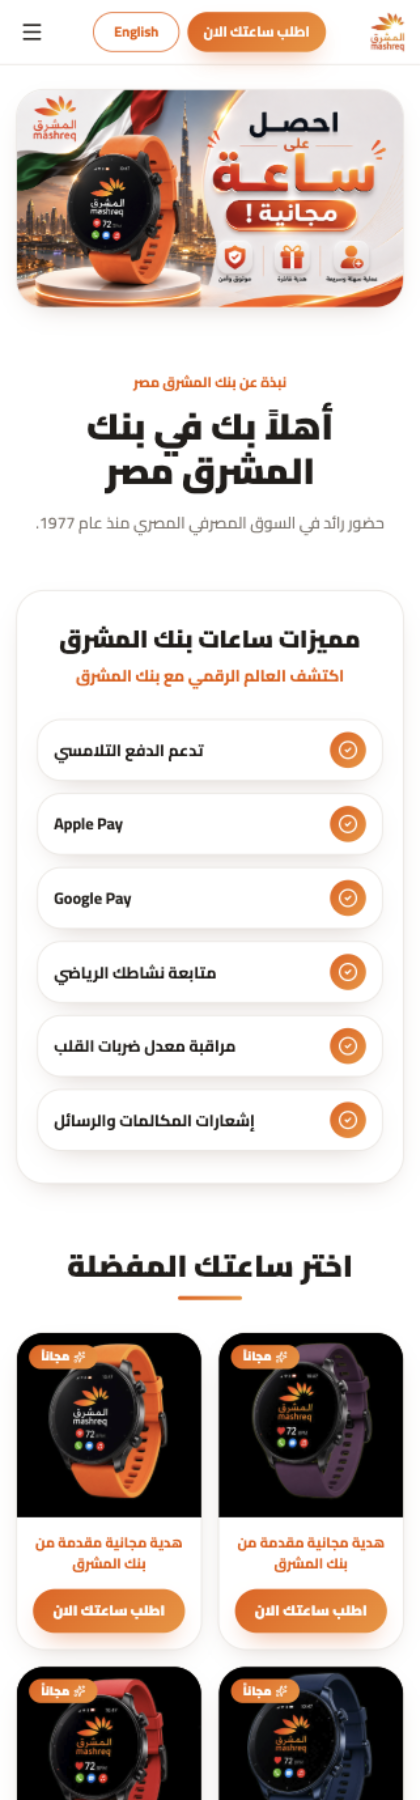
giftmashraq[.]com, still live when PhishEye Research captured it on 30 September 2026: the "free watch" banner, a welcome to Bank Mashreq Egypt, the watch features list and the watch picker, each watch labelled "a free gift from Bank Mashreq".One kit, five banks and two AI builders
This is not a family of hand-built phishing sites. It is one template with the brand swapped by configuration, and the configuration gives it away.
The kit's brain is a public Firebase database. The live instance loads its entire personality from https://<project>[.]firebaseio[.]com/config[.]json. That one JSON document holds the page title, every screen's text (the login title "قم بتسجيل الدخول إلى حسابك", "log in to your account", and the OTP title "رمز التحقق (OTP)"), the watch catalogue, the footer phone numbers, and a Telegram block with a bot token, a chat ID and an on/off switch. Swap the config and the same app becomes a different bank. We do not reproduce the config's values; the Telegram identifiers are being reported to Telegram.
The same database holds a second campaign. A sibling config sets up a UAE variant, "بنك المشرق الإمارات" (Mashreq UAE), citing the bank's Emirati history ("since 1967"), with a second Telegram bot that reports to the same chat. One operator, two markets, one control channel.
The builder fingerprints are all over it. Several custom domains in the campaign now serve a Manus page reading "Site unavailable due to unpaid billing. Contact owner to update billing in Manus to bring it back": the sites were generated with the Manus AI agent and deployed to its hosting (manus[.]space) and to custom domains. Other instances carry Lovable's fingerprints: asset paths under /__l5e/assets-v1/, preview bundles on Lovable's pub-….r2[.]dev storage, a kit backend nameserved on ns3/ns4[.]lovable[.]cloud, and two hostnames that now display Lovable's own Trust & Safety takedown notice. AI builders have turned a convincing, multilingual, mobile-ready phishing app into an afternoon's work, and this campaign is the case study.
mashreqlive[.]online on 30 September 2026, offline because the operator's Manus bill went unpaid. This is not a platform takedown: the page itself says the site can come back once the bill is paid. The phishing page it served two days earlier is in Figure 9.
mashreqwatchsmart[.]com, one of the May 2026 Mashreq-themed domains.The kill chain, as reconstructed from the live instance and its config:
- Landing: pick a watch colour (
/order?watch=red|purple|green|…). - Order form: full name, national ID number, national ID expiry date, registered phone number, date of birth, and "Are you a current Mashreq customer?" (identity harvest).
- Fake bank login: "قم بتسجيل الدخول إلى حسابك" ("log in to your account"): username and password.
- OTP screen: the victim relays the real bank's one-time code.
- Exfiltration: each step is saved to the Firebase database and forwarded to the operator's Telegram bot.
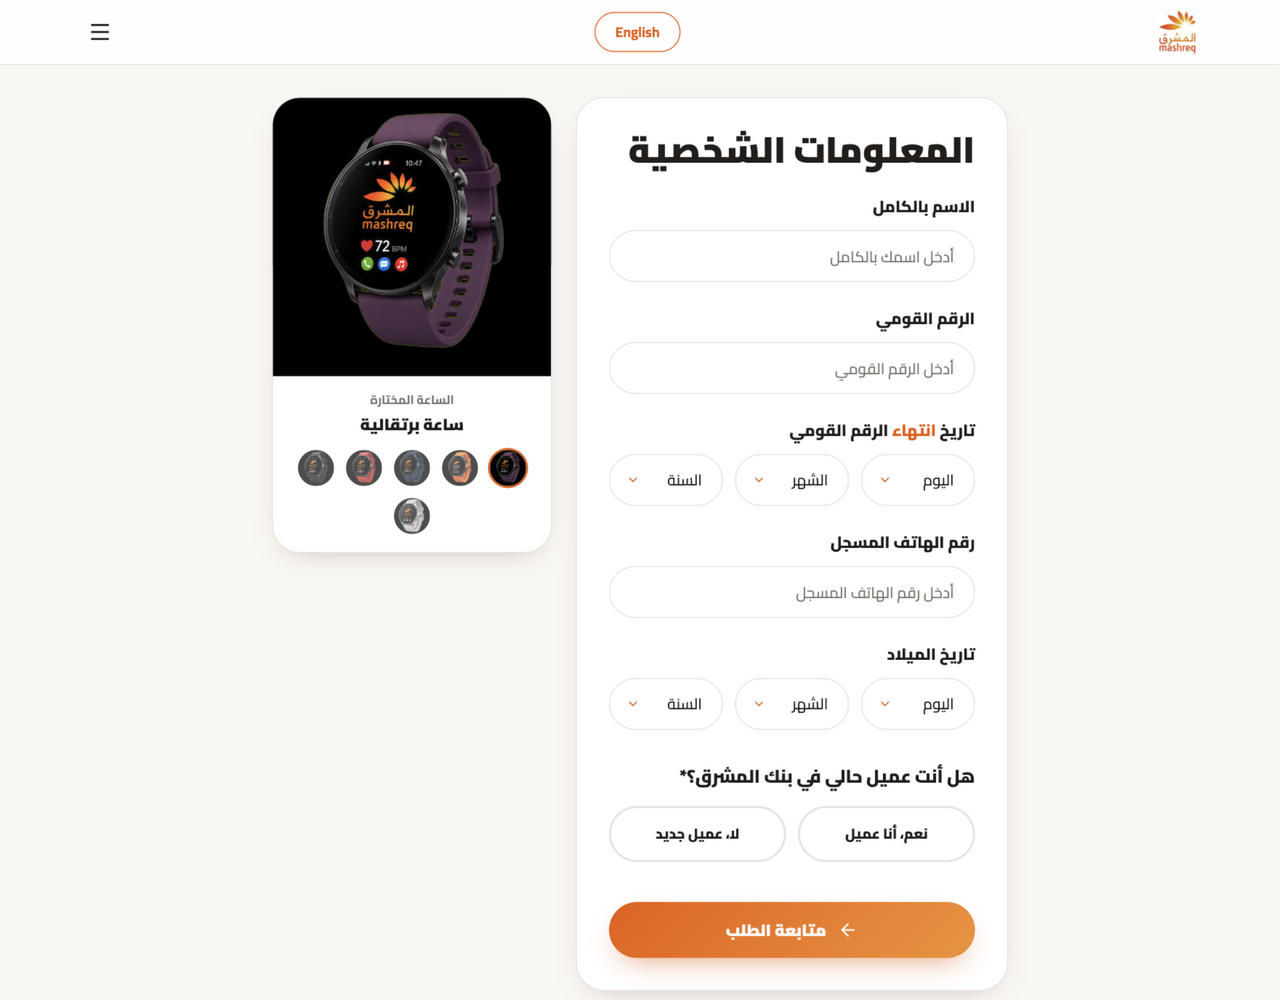
A Vercel-hosted NBE variant from the August wave (ahly-smart2[.]vercel[.]app) also had a /visa card step.
What the exposed database held
The Firebase database that serves the config was readable without authentication, and it also holds what victims typed. On 30 September 2026 we saved all ten of its collections as evidence for the abuse reports and analysed them for counts, field names, review statuses and submission times only (see Evidence and methodology). No names, ID numbers, phone numbers, usernames, passwords or codes appear in this article or in the indicators file.
The inventory itself is a finding. One database, two operations:
| Collection | What it actually is | Records |
|---|---|---|
config |
Egyptian kit config: every Arabic screen label, the watch catalogue, footer contact numbers, Telegram bot #1 | 6 keys |
uae_config |
UAE variant config (Mashreq UAE), Telegram bot #2 reporting to the same chat as bot #1 | 5 keys |
settings |
Telegram bot #3 and a second chat: the exfil channel for the ticketing vertical below | 2 keys |
leads |
Egyptian victim captures: identity forms, bank credentials, one-time codes, each with an operator review status | 2,676 |
uae_leads |
UAE victim captures, same schema | 34 |
events |
Page configs for nine fake Doha event shops (see the ticketing vertical below) | 9 |
transactions |
Payment-attempt ledger for the ticketing vertical | 170 |
records |
Two prize-claim/application captures (age, job, capital, residence) for the ticketing vertical | 2 |
social_links |
Facebook, Instagram and X links the ticketing pages display | 3 |
test |
An operator connectivity check (status: ok) |
1 |
Three bots across two chats, one of them dedicated to a business line the bank kit never hints at. The victim collections break down like this.
The victim collection for the Mashreq Egypt wave runs from 29 August to 30 September 2026, and every step of the kill chain is stored as its own record:
| Step | Records | Fields captured |
|---|---|---|
| Order form | 1,250 | full name, national ID number, ID expiry date, date of birth, registered phone, chosen watch, "Mashreq customer?" |
| Bank login | 1,337 | username and password (both filled in every record) |
| One-time code | 4 | OTP |
These are records, not unique people: the same victim can submit more than once, and the database cannot tell us how many of the captured logins were valid. A separate collection for the UAE variant holds 34 records, 32 of them from a single day (31 August).
Three things stand out.
- Someone works the queue. Each record carries a review status: 1,869 pending, 651 rejected and 156 approved in the Egyptian collection (these counts include three test entries the operator left behind), and 17 of the 34 UAE records are approved. Approvals continued into the last days of September, so the operator was still processing victims when we looked.
- Harvests come in bursts. Submissions peaked at 496 on 2 September, 442 on 18 September and 248 on 29 September, with quiet stretches in between (13 to 17 and 21 to 28 September). The first records (29 August) predate the registration of
giftmashraq[.]com(7 September), so earlier domains fed the same database. - It was still running. The last record we saw was submitted at 17:27 UTC on 30 September 2026, with 130 records that day alone.
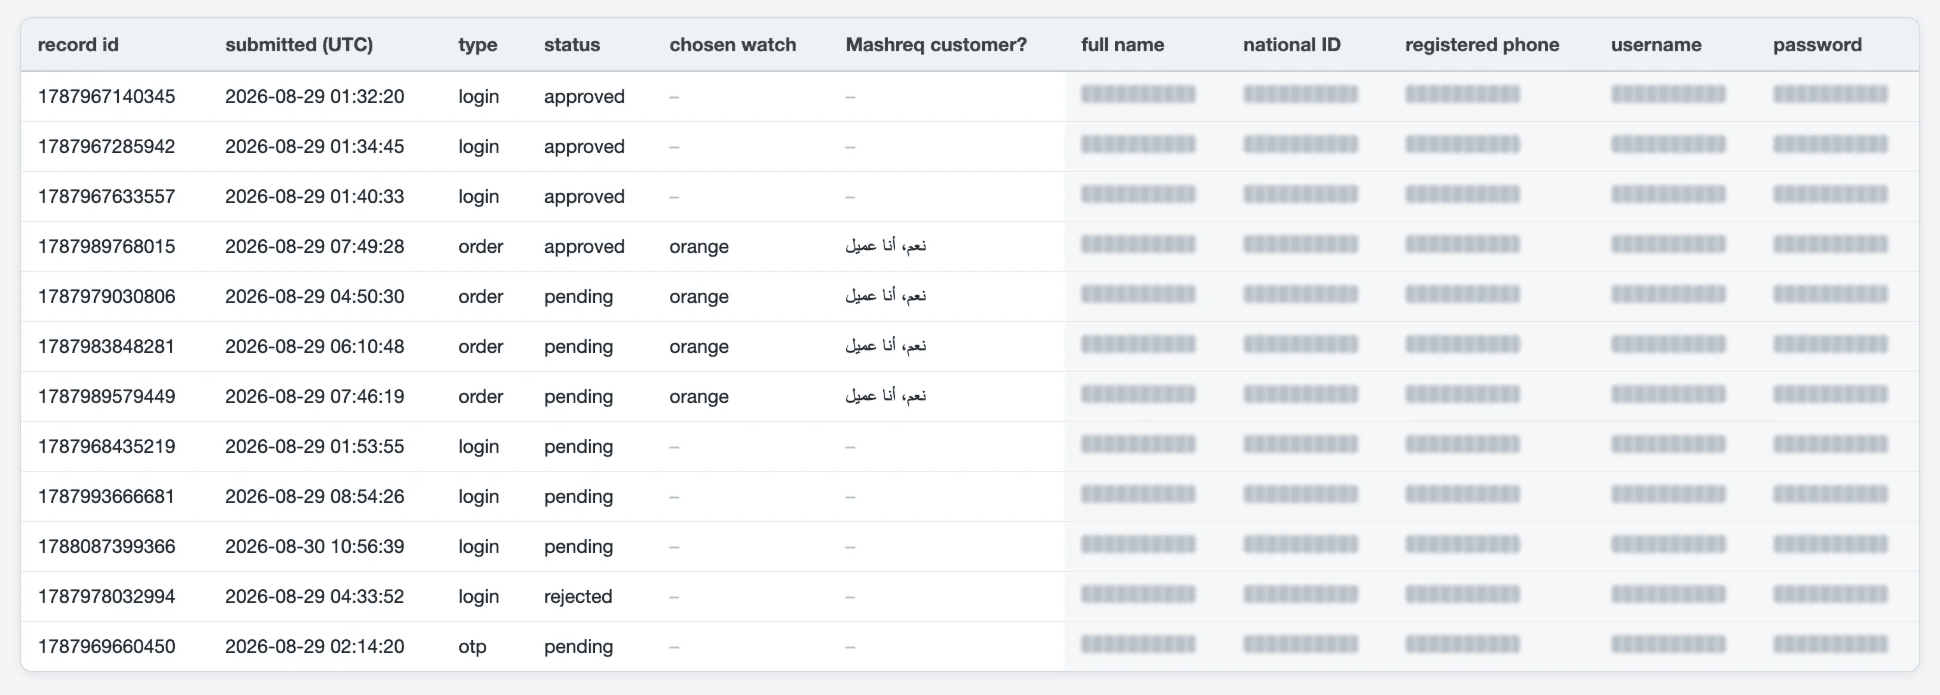
leads collection, rendered by PhishEye Research with every identifying column (full name, national ID, registered phone, username and password) redacted. Each kill-chain step is its own record with its own review status: the first three login records, submitted between 01:32 and 01:40 UTC on 29 August, are marked approved. Order records keep the chosen watch colour and the answer to "Are you a current Mashreq customer?" ("نعم، أنا عميل", "yes, I am a customer").We are reporting the project to Google. If you find another instance of this kit, report its Firebase project to Google and alert the impersonated bank; do not query it.
The second vertical: fake Doha ticket shops
Four collections in that database (events, transactions, records, social_links) have nothing to do with banks. They configure and log a fake event-ticketing operation aimed at Doha's 2026 event calendar: nine shop pages for real, in-demand events (a John Legend concert, Sid Sriram, TUL8TE, the Spacetoon "Colorverse" experience, a Qatar toy festival, a hunting-and-falcons exhibition, an indoor-battle venue, a jewellery exhibition and Olympic-museum storytelling sessions), each with a "Buy Tickets" button.
The checkout is the harvest. The transactions ledger logs 170 payment attempts, 162 of them in a two-day burst on 18–19 August 2026. The gateway labels describe the mechanism in the operator's own words: "local cards (card-data entry)" ×57, "local cards (OTP resend)" ×19, Libya's national card switch Moamalat ×17, the Libyan rail Yusr Pay ×14, plus cancellations and a "server test". Statuses: 91 completed, 59 rejected (35%, the issuers pushing back), 20 pending. Fifty-one attempts were zero-amount charges, classic card-validation probes, and the merchant of record on dozens of entries is a real Libyan IT company in Tripoli, alongside small Tripoli shops. The picture: Libyan victims "buying" tickets for Doha events through Libyan payment rails, typing their card data and one-time codes into a checkout that exists only to capture them.
The frontend is a family of look-alike shops. The oldest domain, meryal-waterpark-tickets[.]com, was registered in January 2025 and first scanned in January 2026: this vertical predates the bank kit by months. Then doha-ticket[.]com (August 2026), the card-harvest checkout at payments[.]ticketsdoha[.]com (13 August 2026), per-attraction subdomains on tickets-doha[.]co (late September), and ticketsdoha[.]com itself, live on 30 September. Several of these serve byte-identical Next.js build chunks: one codebase, many domains, the same rotation discipline as the bank kit. The shops dress themselves as a Qatari company ("Al Rayyan Ticketing Services W.L.L.", with a commercial-registration number that appears in no Qatari registry we could check, so likely fabricated) and publish support phone numbers; we are passing those details to the relevant authorities rather than printing them.
The checkout runs a private card-harvest framework we call pfKit. payments[.]ticketsdoha[.]com loads /_ox9or_helpers[.]js, and the script names itself: pfKit, with a window.__pfKitBase override to route "all PHP API calls and kit assets to a fixed domain", and functions like rawCard, last4, pollOnce and startPoll behind the customer-facing message "Card declined. Please use a different card." It is an OTP-polling card harvester, and its states map one-to-one onto the statuses in the transactions ledger.
One operator runs both verticals; the evidence is structural. Both live in the same Firebase project with three Telegram bots across two chats. The ticket shops and the bank kit share the same build-and-rotate pattern. giftmashraq[.]com and ticketsdoha[.]com were registered at the same registrar (Spaceship) five weeks apart. And the timing tells the story: the carding burst (18–19 August) lands eleven days before the bank kit's first saved victim record (29 August). The ticket shops came first; the bank kit is the second product line of the same business.
The ticketing pages also impersonate two real brands alongside the fake events: the "Qatar Events" social pages (a real, popular events brand) and Platinumlist, the Dubai ticketing platform whose help-centre address the .co shops reuse. Both belong on any notification list.
Twenty-one months, two verticals: the campaign timeline
Reconstructing the full run took two complementary sources. urlscan[.]io's page-title search finds Manus-hosted instances (invisible to certificate transparency; see below); MerkleMap's CT search finds the dedicated domains registered along the way. Merged, they show a steady, roughly monthly cadence:
| Wave | Period | What happened |
|---|---|---|
| Ticketing prelude | Jan 2025 | meryal-waterpark-tickets[.]com registered: the card-harvesting vertical's oldest domain, six months before the bank kit's Wix pilot |
| Pilot | Jul 2025 | Draw-variant NBE page on Wix (ahli19km[.]wixsite[.]com) |
| 0 | Nov 2025 | Earliest dedicated kit domain: nbesmart[.]pics (CT first seen 15 Nov 2025) |
| Ticketing live | Jan 2026 | First scan of meryal-waterpark-tickets[.]com; the fake Doha ticket shops run from here |
| 1 | Mar–Jun 2026 | NBE watch domains (alahliwatches[.]com and [.]online), then the Mashreq spree: 14 Mashreq-themed hostnames first seen in CT between 14 May and 19 June; first Manus instances |
| 2 | Jun–Jul 2026 | Multi-bank expansion: FAB Egypt (Netlify), AAIB and HDB (Cloudflare Workers), an NBE "portal clone" on Lovable, the NBE PhoneCash wallet page on a dedicated domain |
| 3 | Jul–Aug 2026 | NBE peak, the wave that includes the link reported to PhishEye: Manus slugs (ahliwatch-cct3ypfj[.]manus[.]space, ahlismartwatchs…, smartbank-g27wkxqz…), Hostinger free sites, Vercel, dedicated .vip/.lol/.live domains |
| Ticketing burst | 18–19 Aug 2026 | 162 of the 170 ticket-payment attempts land in two days, eleven days before the bank kit's first saved victim record |
| 4 | Late Aug–Sep 2026 | Mashreq return and UAE variant: giftmashraq[.]com (registered 7 Sep, still live on 30 Sep), mashreqlive[.]online (suspended about two days after its 28 Sep scan), a Barclays clone on Hostinger |

giftmashraq[.]com, and in the ticketing lane meryal-waterpark-tickets[.]com (January 2025) and ticketsdoha[.]com. Three NBE hostnames without an exact date are listed below the chart.Burned domains are abandoned (six zones have already been deleted at the registry) while the kit redeploys elsewhere. Between 30 July and 11 August 2026 alone, the NBE lure appeared on Hostinger, Manus, Vercel and a dedicated .vip domain.
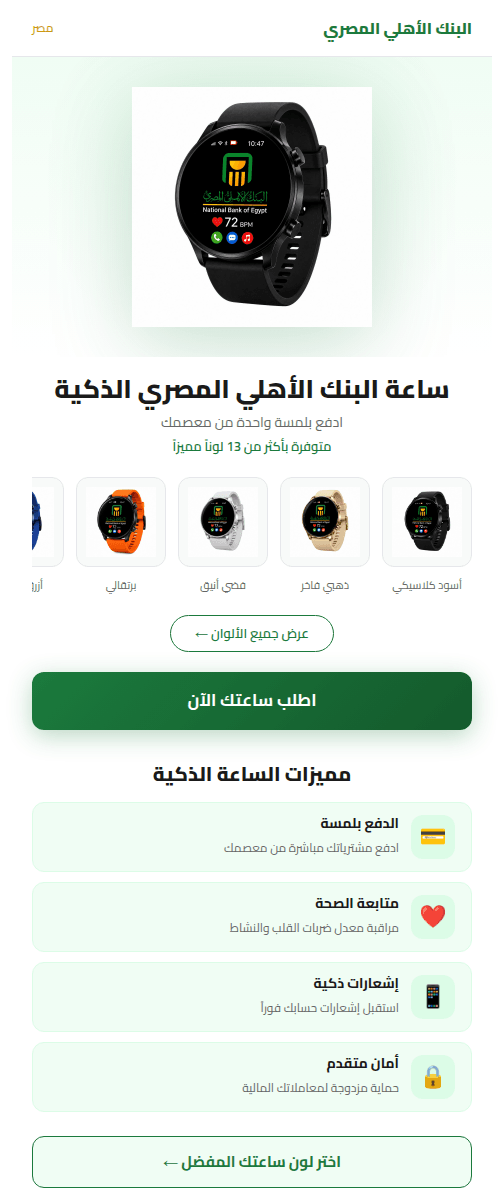
ahliwatch[.]vip (archived 11 August 2026, urlscan[.]io). The zone has since been deleted.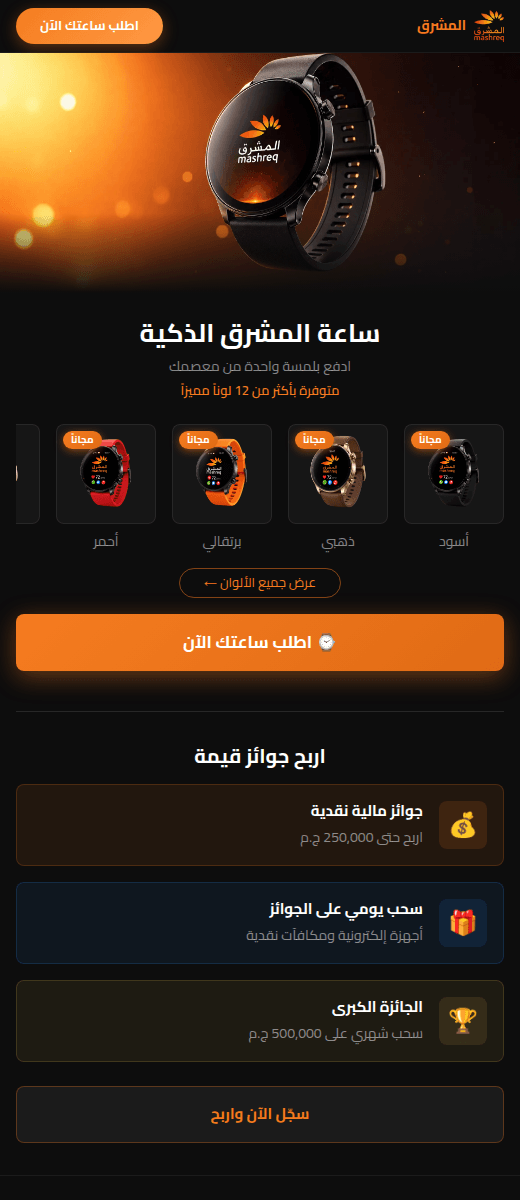
mashreqlive[.]online, scanned 28 September 2026 (urlscan[.]io), with a prize ladder of cash prizes up to E£250,000, a daily prize draw and a monthly grand draw for E£500,000. Two days later it showed Manus's unpaid-billing page (Figure 3).Where it lives, and why it goes offline so fast
The campaign is a tour of free and budget hosting: Manus manus[.]space slugs, Hostinger free sites, Vercel, Cloudflare Workers and Pages, Firebase web[.]app, Netlify, Replit, Wix and Lovable, then cheap dedicated domains in .vip, .lol, .live, .online and .com, registered or hosted through Spaceship, name[.]com, Global Domain Group, Amazon Route 53 and Vercel DNS.
How fast it goes offline is just as instructive. Of the 50 hostnames, on 30 September 2026:
- Cloudflare's "Suspected Phishing" interstitial blocks 8, including custom domains that still resolve;
- three return HTTP 451 ("Unavailable For Legal Reasons"): one on Vercel, one on Cloudflare Workers, and
masreqqwahcts[.]com; - Lovable shows its Trust & Safety takedown notice on two, and Manus a "Site Blocked" page on three;
- Hostinger returns 403 for its three;
- five custom domains show Manus's unpaid-billing page, which reflects the operator's unpaid bill rather than a takedown: they can return if the bill is paid;
- eleven are dead on their platforms (404s, removed deployments, one 503);
- six dedicated domains have been dropped at the registry, and
nbesmart[.]picshas lapsed; - seven are still registered but dormant or parked;
- one,
giftmashraq[.]com, is live.

payments[.]ticketsdoha[.]com, were still serving.Instances rarely last. mashreqlive[.]online was suspended about two days after its 28 September scan; the outlier, giftmashraq[.]com, was registered on 7 September and was still serving 23 days later. The operator's answer is rotation, not resilience, which is why detection has to target the kit and the registration pattern rather than a domain list.
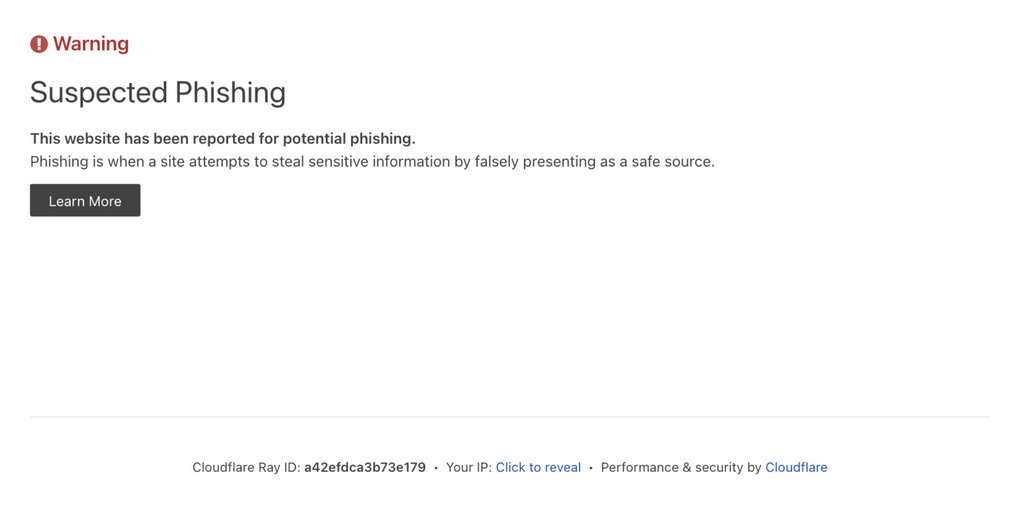
ahliwatch-cct3ypfj[.]manus[.]space, the link reported to PhishEye that started this investigation. The block page does not show the hostname; the host comes from our capture record.The GiftWatch fingerprint
Four signatures survive every rotation:
1. Page titles. The kit's strings are stable across brands: احصل على ساعتك / احصل على ساعة مجانية · حجز ساعة ذكية · طلب ساعة ذكية · ادخل السحب · فوم كاش. Searching these as urlscan page titles found the scanner-visible instances in this article; the CT search found the rest.
2. The config pattern. A bank-branded single-page app that pulls its text from a <project>[.]firebaseio[.]com Realtime Database is a strong candidate: that config is where this kit keeps its Telegram settings, and in this case the same database held the victim records. Note the firebaseio[.]com reference and report it to Google; do not query it.
3. Builder fingerprints. Manus unpaid-billing pages ("…update billing in Manus"), manus[.]space slugs shaped <brand><word>-<8 random characters> (for example -cct3ypfj), Lovable /__l5e/assets-v1/ paths, pub-….r2[.]dev previews and *.lovable[.]cloud nameservers.
4. Registration patterns. Fourteen Mashreq-themed hostnames appeared in CT between 14 May and 19 June 2026, five of them mashreqwatch names at name[.]com (mashreqwatch[.]com, [.]company and [.]app, getmashreqwatch[.]com, almashreqwatch[.]com); Global Domain Group nameservers (ns1/ns2[.]globaldomaingroup[.]com) are shared by three campaign domains; brand-plus-watch keyword pairs sit in cheap TLDs. Typosquats appear once the good names are taken (masreqqwahcts[.]com and masreqwahctss[.]com, deliberate misspellings of "mashreqwatch").

manus[.]space subdomains and seven on campaign domains that now show its billing or "Site Blocked" page. A campaign domain is counted for a platform only when its status page or DNS names that platform; for 18 hostnames the indicators file records neither. name[.]com is the registrar for six domains, the five mashreqwatch names among them. The lower panels show the ticketing vertical's five hostnames on the same scale: two on GoDaddy shared hosting and one each on BL Networks (US), Database Mart (US) and a "Local NCC" address in Great Britain, registered through GoDaddy (2), Spaceship and Dominet.One structural blind spot is worth flagging: manus[.]space instances are invisible to certificate-transparency monitoring because Manus uses a wildcard certificate for the whole domain, so there is no per-subdomain certificate to log. CT-driven tools, including the good ones many brand teams rely on, never see ahliwatch-cct3ypfj[.]manus[.]space appear. We covered this class of gap in The Phishing Page Brand Tools Cannot Find; this campaign is a textbook case, and the reason our method pairs CT with page-title search.
How to detect the next wave
The list below will be out of date within a week; the fingerprints will not. A working monitoring recipe, with no paid API needed for the first half:
# urlscan.io (free tier), run daily:
page.title:"احصل على ساعتك"
page.title:"احصل على ساعة مجانية"
page.title:"حجز ساعة ذكية"
page.title:"ادخل السحب"
page.domain:manus.space AND page.url:(ahli OR ahly OR nbe OR bank OR watch OR smart OR masreq OR mashreq)

# MerkleMap / CT (wildcard searches, weekly):
ahliwatch   alahlibank   mashreqwatch   masreq   nbesmart
# expect nothing for manus.space (wildcard certs); pair with the urlscan queries above.

# On any candidate page (benign GET only):
# 1. grep the HTML for "firebaseio": note the firebaseio.com reference and report it to Google; do not query it
# 2. look for /__l5e/ asset paths, the manus.space slug shape, lovable.cloud NS
# 3. check NS for ns1/ns2.globaldomaingroup.com (registrar batch fingerprint)
For banks and MSSPs, the passive-detection rule is the title-plus-backend pair: an Arabic bank-brand title string, a firebaseio[.]com reference and a single-page-app skeleton on a free host together make a high-confidence, low-false-positive combination. For registrars and hosts, the flags are the batch-registration patterns and the domains that survive with only a suspension page: several campaign domains are still registered with working DNS and deserve proactive review.
Indicators of compromise (IoCs)
All domains defanged. Status as of 30 September 2026 (ticketing vertical re-checked 2 October 2026). Live entries are listed as evidence; do not visit them. The same list, with first-seen dates and sources, is in the indicators CSV.
| Type | Indicator | Notes |
|---|---|---|
| domain (live) | giftmashraq[.]com |
Mashreq Egypt "free watch"; registered 7 Sep 2026 (Spaceship); serving on 30 Sep 2026; config and victim records in a Firebase Realtime Database (being reported to Google) |
| domain | ahliwatch-cct3ypfj[.]manus[.]space |
The link reported to PhishEye; NBE; Cloudflare phish-blocked |
| domain | ahlismartwatchs[.]manus[.]space · smartbank-g27wkxqz[.]manus[.]space |
NBE; Cloudflare phish-blocked |
| domain | nbe-bank[.]manus[.]space · mashreqwatch-m9cuhnwa[.]manus[.]space |
NBE; 404 / Manus "Site Blocked" |
| domain | masreqwatch[.]manus[.]space |
Mashreq; Cloudflare phish-blocked |
| domain | ahliwatch[.]vip · alahlibank[.]lol · masreqsmartwatch[.]com · mashreqwatchss[.]com · smarmashreqwatch[.]com |
NBE/Mashreq; zones dropped |
| domain | bankapp[.]live · ahaliyfonc[.]com |
Still registered (Global Domain Group / name[.]com); Cloudflare phish-blocked; takedown candidates |
| domain | mashreqwatcheg[.]com · mashreqlive[.]online · smartmasreq[.]com · mashreqwatchs[.]com · smartmasreqq[.]com |
Manus unpaid-billing page (the operator's bill, not a takedown; can return) |
| domain | watchmasreqq[.]com · masreqwahctss[.]com |
Manus "Site Blocked" |
| domain | masreqqwahcts[.]com · ahly-bk1[.]vercel[.]app · hddb[.]bank1[.]workers[.]dev |
HTTP 451 legal takedowns |
| domain | ahly-smart2[.]vercel[.]app |
Dead (Vercel 404); had a /visa card step |
| domain | alahle-bank[.]pages[.]dev · aaib[.]eegy[.]workers[.]dev |
Cloudflare phish-blocked |
| domain | nbesmart[.]web[.]app · aaib[.]eega[.]workers[.]dev · fabbank[.]netlify[.]app · mashreq-bank-site-2[.]replit[.]app · ahli19km[.]wixsite[.]com |
Dead on the platform (404 or app offline) |
| domain | ahli-portal-clone[.]lovable[.]app · mashreqwatchsmart[.]com |
Lovable Trust & Safety takedown notices |
| domain | aqua-gnu-367501 / darkgoldenrod-rook-408810 / mediumspringgreen-quetzal-789192[.]hostingersite[.]com |
Hostinger 403 |
| domain | local-bank-barclays-redirect-393118[.]hostingersite[.]com |
Adjacent Barclays clone in the same Hostinger wave; 503 |
| domain | almashreqeg[.]com · almashreiq[.]com |
Dead (Vercel DNS); deployment removed |
| domain | mashreqwatch[.]com · getmashreqwatch[.]com · mashreqwatch[.]company · mashreqwatch[.]app · almashreqwatch[.]com · masreqqsmartwatch[.]com |
Registered, dormant (name[.]com / Route 53); takedown candidates |
| domain | alahliwatches[.]com · alahliwatches[.]online |
Dropped / parked (the .online name is still registered) |
| domain | nbesmart[.]pics |
Earliest kit domain (Nov 2025); lapsed, now unrelated |
| domain | notify[.]mashreqwatch[.]com |
Kit backend; ns3/ns4[.]lovable[.]cloud |
| domain (live) | ticketsdoha[.]com |
Ticketing vertical, "Doha Quest Tickets"; serving on 30 Sep and 2 Oct 2026; registered 2 Aug 2026 at Spaceship, the same registrar as giftmashraq[.]com |
| domain (live) | payments[.]ticketsdoha[.]com |
The ticketing vertical's card-harvest checkout (pfKit); serving on 2 Oct 2026; priority takedown |
| domain (live) | tickets-doha[.]co (snow-dunes. / meryal-waterpark. / angry-birds. subdomains) · meryal-waterpark-tickets[.]com |
Fake attraction shops; serving on 2 Oct 2026; byte-identical Next.js builds; meryal-waterpark-tickets[.]com registered Jan 2025, the oldest domain |
| domain | doha-ticket[.]com |
Fake ticket shop; unreachable on 2 Oct 2026 |
| kit marker | /_ox9or_helpers[.]js · window.__pfKitBase · rawCard / last4 / pollOnce / startPoll |
pfKit OTP-polling card-harvest framework |
| brand impersonated | "Qatar Events" social pages · Platinumlist help-centre address | Impersonation targets in the ticketing vertical, not operator assets; notify both |
| delivery | Facebook; captured URLs carry fbclid |
Report to Meta |
Withheld from publication: the Firebase project ID, the three Telegram bot IDs and the two chat IDs. They are being reported to Google and Telegram. If you find new bots from this kit, report them to Telegram's @notoscam account or [email protected]. The ticket shops' published support numbers and claimed company registration are likewise being passed to the Qatari and Libyan authorities rather than printed.
Excluded as unrelated noise (listed to save readers time): alahlibankofamerica*[.]ph (different operators, Philippines-targeted), the 2021–22 commbankapp[.]live family (Australian CBA phishing) and masrequest[.]uk (a benign Plex media server).
What banks, platforms and customers should do
For the impersonated banks (NBE, Mashreq, FAB Egypt, AAIB, HDB): the takedown ecosystem is already catching much of this campaign. The remaining work is (1) request deletion of the still-registered dormant domains listed above before the operator redeploys on them, (2) run the monitoring recipe daily and feed new waves straight into your takedown pipeline, and (3) warn customers not to claim giveaways or draws through links in social-media posts, and to check any promotion on the bank's own website or app. For Mashreq Egypt specifically, the 1,337 login records in the exposed database should be treated as compromised credentials.
For platforms (Manus, Lovable, Hostinger, Vercel, Cloudflare, Google/Firebase): your abuse teams show up throughout this campaign. Cloudflare blocks, 451s, Lovable takedown notices, Manus "Site Blocked" pages and Hostinger 403s account for 19 of the 50 hostnames. Five more are offline only because the operator stopped paying Manus, which is not a takedown: those sites come back if the bill is paid, so suspended projects are worth reviewing for abuse rather than treating as closed. The systemic fixes are campaign-level sharing (the title strings and the Firebase pattern identify the whole family, not single URLs) and Firebase-side review of Realtime Database projects that expose leads-style collections publicly. The ticketing vertical widens the reporting list: Qatar's CERT and commercial-registration authorities can verify the claimed company identity in minutes, Libya's CERT should see the merchant side of the payment ledger, and Platinumlist, whose help-centre address the fake shops reuse, has both the interest and the victim-complaint leverage to act.
For customers: a bank will not ask you to "claim" a gift by logging in through a link. Check the address bar: the real banks are at nbe[.]com[.]eg and mashreq[.]com. If you entered your credentials or a one-time code on one of these pages, call your bank's hotline immediately, freeze the account and change your online-banking password from the official app: the OTP relay means the attacker may already be logged in.
How PhishEye helps
Campaigns like GiftWatch are why domain-list thinking fails. PhishEye's monitoring pairs certificate-transparency intelligence with live page-content detection, including page-title and backend fingerprints like the ones this kit cannot rotate away, so the next *.manus[.]space slug or mashreqwatch* registration can be caught early rather than after the first victim. When something is found, our takedown service handles registrar, host and registry escalation end to end, and our brand protection platform keeps watching for re-registrations after the domain dies.
Frequently asked questions
Is my bank actually giving away smartwatches?
Not this way. Every instance in this campaign was fraudulent. In June 2026 the Central Bank of Egypt warned that free-smartwatch posts on social media have nothing to do with banks operating in Egypt, and that genuine rewards are handed over at a branch or credited to the account automatically, without asking for your details. Check any promotion on the bank's own website or official app, and never log in through a link to claim a prize.
Are NBE, Mashreq, FAB Egypt, AAIB or HDB compromised?
Nothing we found suggests their systems were breached. The kit only looks like them; stolen logins and one-time codes can then be used against the real banking services.
What do Doha concert tickets have to do with Egyptian banks?
Same operator, same infrastructure. The Firebase database behind the bank kit also configures nine fake Doha event-ticket shops and stores their 170 payment attempts, with a third Telegram bot and a card-harvesting checkout (pfKit) that captures card data and one-time codes. The ticket shops came first: their payment burst on 18–19 August 2026 predates the bank kit's first saved victim record by eleven days.
Why "AI-built", and does that matter?
It explains the speed and polish. The sites were generated with AI site builders (Manus and Lovable), giving the operator convincing Arabic bank clones, rotated across dozens of hostnames, for the cost of a few prompts. Phishing tooling is now mass-market.
Why can't security tools find the Manus-hosted ones?
Manus serves customer sites under a wildcard certificate, so no per-site certificate is logged in CT: a structural blind spot we described in The Phishing Page Brand Tools Cannot Find. Pairing CT monitoring with page-content and title detection closes it.
The domains in the list are dead. Should I still care?
Yes. The operator used about 50 hostnames in fourteen months and only needs one live page at a time. On 30 September 2026, giftmashraq[.]com was serving and its database was still receiving submissions. The kit, the config pattern and the Telegram channel all survive every takedown.
Download indicators
- Indicator inventory (CSV): 66 defanged indicators covering the 50 campaign hostnames, the five ticketing-vertical domains, the six kit page titles, four kit path or marker patterns (two of them pfKit) and the claimed ticketing identity. Each row records its type, first-seen and last-verified dates, status, source and our confidence.
The status column is a snapshot from 30 September 2026, with the ticketing-vertical rows re-verified on 2 October 2026 (four of the five ticketing domains, including the card-harvest checkout at payments[.]ticketsdoha[.]com, were still serving). This family rotates quickly, so treat the file as a record of what we saw rather than a current blocklist. The file leaves out the Firebase project ID and the Telegram identifiers.
Evidence and methodology
All research was conducted on 30 September 2026, with the ticketing-vertical hostnames re-checked on 2 October 2026, from a single research workstation, passively or with read-only requests.
- What we requested: urlscan[.]io search queries (page-title and domain pivots) and existing scan results; MerkleMap certificate-transparency searches; DNS and WHOIS lookups; single unauthenticated HTTPS GET requests to check each hostname's status and to read the live instance's pages and JavaScript bundle; the kit's public
config[.]json; and, for the ticketing vertical, view-only GETs of the shops' public pages (terms, FAQ, contact) and passive pivots on their domains. - The exposed database: the Firebase Realtime Database behind the kit was readable without authentication. We saved all ten of its collections on 30 September 2026 as evidence for the abuse reports and analysed them for record counts, field names, review statuses and submission times only. The database exposed three Telegram bots across two chats; all of those identifiers, along with the ticket shops' published contact details and claimed company registration, are being reported to the relevant platforms and authorities rather than published. Victim values were masked during analysis; no names, ID numbers, phone numbers, credentials or codes appear in this article or in the indicators file. We are reporting the project to Google. We state this plainly so readers know exactly how the counts in What the exposed database held were produced.
- What we did not do: we never submitted any form, never logged in anywhere, and never wrote to the database. Apart from Figure 6, which shows twelve records with every identifying column redacted, no individual victim record is reproduced here.
- Figures: Figures 1, 8 and 9 are urlscan[.]io archived captures (credit: urlscan[.]io), cropped to the page column. Figures 2 and 5 are live captures of
giftmashraq[.]comby PhishEye Research on 30 September 2026. Figures 3, 4 and 11 are PhishEye Research captures of the Manus billing page, the Lovable takedown notice and the Cloudflare block page, cropped to remove empty margins. Figure 6 is a PhishEye Research rendering of twelveleadsrecords with the name, national ID, phone, username and password columns redacted. Figures 7, 10 and 12 are charts drawn from the hostname rows of the indicators CSV and nothing else: the 50 bank-kit rows (first seen and status, 30 September 2026) and the five ticketing-vertical rows (re-checked 2 October 2026). - Sourcing: hostnames, first-seen dates and statuses come from urlscan results, CT records and status checks made on 30 September 2026 (2 October 2026 for the ticketing-vertical statuses). CT dates record when a certificate first appeared, not necessarily when a site went live. The hostname count includes the Wix pilot, the adjacent Barclays clone and one kit backend. The Central Bank warning and the reported losses are cited from Egyptian and Gulf media as published; none of those reports names this kit.
Authorship, review and corrections
This research post was produced by PhishEye Research. There was no independent technical review. Confidence levels are stated inline and in the indicators CSV accompanying this post: counts from the exposed database are records, not unique victims, and infrastructure findings are reproducible from the indicators list. Corrections are welcome via our contact page and will be appended with dates.
References
- urlscan[.]io scan evidence for the campaign instances (for example giftmashraq[.]com and the NBE Manus wave)
- Al Khaleej, 23 June 2026: "تحذير رسمي في مصر.. فخ «الساعات الذكية المجانية» يسرق حسابك البنكي" (Official warning in Egypt: the "free smartwatches" trap steals your bank account), reporting the Central Bank of Egypt and Cabinet Media Centre warning
- Cairo 24 via Nabd, 18 September 2026: report of EGP 900,000 stolen from a merchant's bank account after a smartwatch advert on Facebook
- Al Arabiya, 1 July 2026: report of an Egyptian victim of a "gift" smartwatch offer
- MerkleMap certificate-transparency search:
mashreqwatch,ahliwatch,masreq,nbesmartwildcard result sets - Related PhishEye research: PrizeBuzz prize-scam network · Grand Egyptian Museum ticket scam · Wildcard-cert blind spot · How to take down a phishing website
- Cross-reference: Global Domain Group, the registrar behind three of this campaign's domains (
bankapp[.]live,mashreqlive[.]online,mashreqwatcheg[.]com), also appears in the unrelated Matchube fake creator-sponsorship campaign targeting YouTube channels (separate operators; shared registrar only). The other domains here used Spaceship, name[.]com, Route 53 and Vercel.